
ISC2's September 2026 India analysis found AI skills were named by 52% of its Indian respondents, cloud security by 43% and application security by 38%. cybersecurity market
2027–2028 research update and source methodology: The ISC2 2025 Cybersecurity Workforce Study surveyed 16,029 professionals across North America, Latin America, Asia-Pacific and EMEA. Its India-specific September 2026 analysis reported AI skills cited by 52% of Indian respondents, cloud security by 43% and application security by 38%; these figures describe that Indian study's respondents and cannot be generalized across Asia-Pacific. National cyber rules, skills demand, cloud investments and breach reporting differ widely between Japan, India, Singapore and other markets. Proprietary 12-country spending figures and exact investment totals from the earlier article lacked a disclosed dataset.
Unlike Europe or the U.S., APAC’s cyber terrain is deeply fragmented. Regulations vary widely, cultural reluctance to report breaches slows response times, and BYOD usage skyrockets with minimal control. Yet, this volatility fuels growth. APAC isn’t just catching up—it’s becoming a proving ground for next-gen cybersecurity vendors, cross-border defense coalitions, and hyperlocalized upskilling programs. Understanding this ecosystem now gives you first-mover advantage in the region’s most high-stakes digital arms race.
Regional Investment Trends
Japan, Singapore, and India Comparison
In 2027–2028, Japan, Singapore, and India are shaping the core of APAC’s cybersecurity investment map—each with vastly different approaches.
- ISC2's September 2026 India analysis found AI skills were named by 52% of its Indian respondents, cloud security by 43% and application security by 38%.
Singapore is focused on becoming a regional cyber innovation nucleus, allocating substantial grants through its Cybersecurity Strategy 2027–2028, including funding for AI-infused threat detection and R&D of quantum-safe encryption.
India leads in volume-based investment, driven by its massive SME and cloud-first ecosystem. The government’s Digital India 2.0 initiative is funneling funds toward SOC modernizations, regional security labs, and public sector cloud hardening.
Asia-Pacific national cyber rules and investment profiles vary. National budget figures and precise breach totals require specific official sources and reporting years.
Government vs. Enterprise Focus Areas
Cybersecurity growth in APAC is split—government funding is policy-driven, while enterprise investments are reactive and rapid.
Governments in the region are investing in:
Regulatory frameworks (e.g., India’s Digital Personal Data Protection Act)
National CERT expansions across ASEAN
Cyber diplomacy programs for cross-border information exchange
Enterprises, particularly in fintech, e-commerce, and logistics, are spending on:
Supply chain security suites
Cloud-native risk scoring platforms
ISC2's September 2026 India analysis found AI skills were named by 52% of its Indian respondents, cloud security by 43% and application security by 38%.
Governments build structure. Enterprises build speed. Both are raising APAC’s cyber maturity fast—but unevenly.

Top Threats in the APAC Region
Nation-State Espionage
ISC2's September 2026 India analysis found AI skills were named by 52% of its Indian respondents, cloud security by 43% and application security by 38%.
Key targets:
Military contractors in South Korea and Japan
Foreign policy institutes in Singapore and Australia
Critical semiconductor and biotech firms in Taiwan
These campaigns often exploit VPN appliances, email gateways, and zero-day flaws in regional CMS platforms. Governments are responding with stricter cyber diplomacy rules, increased attribution capabilities, and supply chain trust frameworks. Still, lack of regional coordination gives adversaries an edge.
Telecom Infrastructure Exploits
Telecom remains one of APAC’s most targeted verticals. With 5G rollout accelerating across India, Thailand, and Vietnam, attackers are exploiting:
SS7 and Diameter protocol vulnerabilities
Unsecured IoT gateways in base stations
Legacy router firmware in rural deployments
ISC2's 2025 workforce survey included 16,029 cybersecurity professionals in multiple regions; it cannot be extrapolated as an Asia-Pacific spending index.
Governments are now mandating telecom-specific SOCs, while startups in Singapore and South Korea are developing air-gapped defense layers for mobile cores.
Small Business Vulnerabilities
Asia-Pacific national cyber rules and investment profiles vary. National budget figures and precise breach totals require specific official sources and reporting years.
Common issues include:
Exposed RDP ports
Unpatched WordPress plugins
No EDR or SIEM in place
Many SMBs in Indonesia, the Philippines, and Vietnam rely on insecure free antivirus tools, and 2FA is rarely enforced. Local governments are piloting cyber hygiene subsidies, but adoption is slow. The result? These businesses become entry points into larger supply chain attacks targeting banks, logistics providers, and government portals.
| Threat Category | Key Targets | Attack Vectors | Regional Impact |
|---|---|---|---|
| Nation-State Espionage | Military contractors, think tanks, policy institutes | APT groups, phishing, credential harvesting | Japan, South Korea, Taiwan |
| Telecom Exploits | 5G base stations, core routers, mobile gateways | SS7 flaws, unpatched firmware, DPI surveillance | India, Vietnam, Thailand |
| Small Business Vulnerabilities | Retail, logistics, hospitality SMEs | Exposed RDP, no EDR, plugin exploits | Philippines, Indonesia, Malaysia |
What Makes APAC’s Market Unique
Cultural Barriers to Reporting Incidents
ISC2's September 2026 India analysis found AI skills were named by 52% of its Indian respondents, cloud security by 43% and application security by 38%.
Reputational risk in collectivist cultures
Fear of government scrutiny or license impact
Lack of legal clarity around breach thresholds
In Japan and South Korea, internal containment is prioritized over public collaboration. In Indonesia and Malaysia, many breaches go completely unreported due to a lack of cybersecurity regulation enforcement. This underreporting cripples regional threat intelligence sharing and slows CERT coordination.
Without cultural shifts and stronger safe harbor laws, breach transparency will continue to lag, leaving the region’s cyber ecosystem exposed.
BYOD and Tech Adoption Speed
ISC2's 2025 workforce survey included 16,029 cybersecurity professionals in multiple regions; it cannot be extrapolated as an Asia-Pacific spending index.
The problem: most of these devices run unpatched Android OS, connect via unsecured Wi-Fi, and lack MDM (mobile device management) policies.
In India, BYOD is prevalent in startups and remote teams
In Thailand and Vietnam, it dominates logistics and field operations
In the Philippines, educational and public health sectors rely on BYOD by default
Rapid cloud adoption compounds the risk. Businesses move fast, but mobile-first setups lack proper access controls, enabling credential theft and lateral movement with ease.
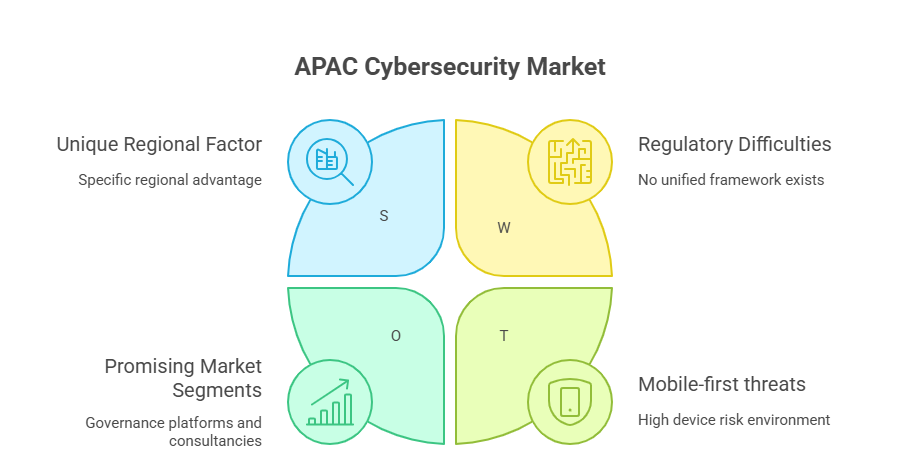
Varied Regulations Across Borders
APAC has no GDPR-style centralized framework—instead, it’s a maze of national rules:
Singapore’s PDPA, India’s DPDP Act, and Japan’s APPI have matured
Vietnam, Thailand, and Indonesia are still formalizing enforcement
China’s CSL and PIPL laws create separate regulatory firewalls
This diversity means multinationals must juggle data residency laws, breach timelines, and compliance audits in up to a dozen languages and legal formats. There is no unified enforcement body, which leads to gaps in cross-border breach response and cloud provider accountability.
For cyber vendors and teams, this creates high compliance overhead—but also opens opportunity for region-specific governance tools and APAC-specialized consultancies.
Emerging Vendors to Watch
Local Players Disrupting the Market
In 2027–2028, APAC-born cybersecurity startups are no longer playing catch-up—they’re setting standards. Countries like Singapore, India, and South Korea are producing homegrown vendors that compete directly with global giants, especially in threat intelligence, IoT security, and data privacy automation.
Notable players include:
Horangi (Singapore) – Specializing in cloud security posture management (CSPM) for Southeast Asian SaaS firms
TAC Security (India) – Offering automated vulnerability management used by several state-backed institutions
SecuLetter (South Korea) – Developing zero-day malware detection for telecom and financial enterprises
CTM360 (Bahrain, APAC-focused) – Leading in external threat surface monitoring for hybrid-cloud deployments
These vendors are winning market share by pricing for local budgets, complying with country-specific regulations, and offering localized language support—a major advantage over U.S.-based competitors.
Cross-Regional Cybersecurity Partnerships
As threats transcend borders, so do alliances. In 2027–2028, we’re seeing a surge in APAC-internal cybersecurity partnerships, as well as intergovernmental collaborations on threat detection and protocol standardization.
Examples:
India-Japan Cybersecurity Agreement focuses on joint defense R&D and AI malware detection labs
ASEAN Cybersecurity Cooperation Strategy supports threat intel exchange between Singapore, Malaysia, Vietnam, and Thailand
South Korea-Australia AI Cyber Challenge Fund is backing post-quantum encryption pilot projects
These partnerships are accelerating vendor maturity and aligning baseline security protocols across divergent regulatory systems. We're also seeing venture capital co-investment frameworks that help vendors scale regionally without relocating, enabling them to retain jurisdictional trust while expanding market share.
The future of APAC cybersecurity is not just about local strength—it’s about strategic alliances that fuse compliance, intelligence, and speed.
| Vendor/Partnership | Country/Region | Specialization | Strategic Advantage |
|---|---|---|---|
| Horangi | Singapore | Cloud security posture management (CSPM) | Local support, SaaS-native tooling, compliance-aligned |
| TAC Security | India | Vulnerability management automation | Used by Indian government; scalable for SMBs |
| SecuLetter | South Korea | Zero-day malware detection | AI-based filtering for telecom and finance sectors |
| CTM360 | Bahrain / APAC-focused | External threat surface monitoring | Cloud-based monitoring for hybrid infrastructures |
| India–Japan R&D Alliance | India & Japan | Joint AI-based malware defense labs | State-backed; enhances threat sharing and tech innovation |
Hiring & Skills Outlook
Regional Certifications Gaining Popularity
In 2027–2028, the APAC region is seeing a surge in localized cybersecurity certification programs. While global credentials like CISSP and CEH remain respected, there’s growing demand for regionally tailored certifications that reflect APAC-specific threats, regulations, and infrastructure realities.
Key programs gaining traction:
CCSP-J (Certified Cloud Security Professional – Japan): Now required by several public sector agencies for compliance readiness
CISA-India Special Track: Aligned with the DPDP Act and covering regional data handling use cases
ASEAN-CERT Cross-Border Readiness Program: A modular initiative focused on breach triage and multi-jurisdiction response
These programs are being embedded in government hiring criteria and vendor compliance frameworks. For cybersecurity professionals, certification selection is now a strategic decision—one that can determine access to regional contracts and cross-border mobility.
Demand for SOC and Cloud Experts
ISC2's September 2026 India analysis found AI skills were named by 52% of its Indian respondents, cloud security by 43% and application security by 38%.
SOC analysts are needed to support 24/7 monitoring for banking, telecom, and logistics clients operating across multiple time zones
Cloud security engineers are critical for SaaS providers and digital transformation programs adopting hybrid-cloud and multi-cloud environments
Top countries driving demand:
India – Scaling rapidly due to startup boom and BPO security outsourcing
Singapore – Hiring for compliance-heavy SOCs tied to government contracts
Australia – Building cloud-native incident response teams for critical infrastructure
Fluency in cloud tooling (e.g., AWS GuardDuty, Azure Sentinel) and SIEM platforms (e.g., Splunk, QRadar) is now considered baseline. Candidates with bilingual skills and regional certification have a distinct advantage in hiring pipelines.

Upskill with Our APAC-Focused Cybersecurity Program
Local Threat Labs + Remote Job Alignment
Training for APAC cybersecurity isn’t just about understanding global frameworks—it requires direct exposure to region-specific threat patterns, legal environments, and infrastructure blind spots. That’s why our Advanced Cybersecurity & Management Certification (ACSMC) by ACSMI is built with localized threat labs and remote job readiness at its core.
The program includes:
Simulated SOC labs built around attacks on APAC-specific targets (e.g., telecom nodes, unsecured RDP, misconfigured e-government platforms)
Real-world response scenarios that reflect fragmented regulatory responses across countries like Indonesia, Vietnam, and Japan
Projects that align with remote hiring demands from APAC-based enterprises in cloud defense, incident triage, and regulatory remediation
Graduates complete the program with the confidence to enter regional hiring pipelines, even if they’re based remotely, thanks to ACSMC’s focus on compliance-aligned, job-ready outcomes.
Certification Based on Regional Data
Unlike global one-size-fits-all programs, ACSMC is built entirely on 2027–2028 APAC data. From threat taxonomies to cross-border case studies, everything reflects real breach trends and enforcement actions across the region.
Key highlights:
GDPR-equivalent policies like PDPA, DPDP, and APPI are mapped into case-based assignments
Labs feature threat vectors found in APAC telecom, logistics, and fintech sectors
Learners engage in multilingual breach simulations for Singapore, India, and Australia-based threat scenarios
This gives professionals a strategic edge when applying to roles that demand regional fluency, cloud expertise, and policy-aligned incident response. Whether you're upskilling in-country or remotely, the ACSMC by ACSMI is built to make you a high-value cyber asset across APAC.
Frequently Asked Questions
-
Asia-Pacific's cybersecurity market is growing faster due to a combination of rapid digital transformation, nation-state cyber threats, and widening regulatory enforcement. Countries like India and Singapore are investing heavily in infrastructure modernization and cloud adoption, while regional conflicts have accelerated the need for defense-grade cybersecurity frameworks. The presence of large populations, emerging tech ecosystems, and fragmented laws means businesses must scale security solutions uniquely tailored to local conditions. Additionally, telecom expansion, 5G rollouts, and AI-driven malware campaigns are pushing both governments and enterprises to prioritize cybersecurity. This multi-layered urgency makes APAC one of the most dynamic—and complex—markets in the world.
-
In 2027–2028, APAC businesses face threats across three tiers: nation-state espionage, telecom infrastructure exploits, and SMB-targeted vulnerabilities. State-backed APT groups are infiltrating military contractors, financial institutions, and think tanks across Japan, South Korea, and Taiwan. Simultaneously, 5G rollouts in Southeast Asia are being compromised through unpatched mobile gateways and outdated firmware in rural networks. Meanwhile, small businesses remain highly exposed, often lacking even basic EDR or MFA protocols. The rapid adoption of cloud and mobile-first operations without strong governance frameworks has expanded the region’s attack surface—making APAC a prime target for cross-border ransomware and credential theft campaigns.
-
Governments in APAC tend to focus on regulatory infrastructure, national threat intelligence platforms, and sovereign SOC deployments. For example, India’s public funding flows toward Digital India 2.0, while Singapore funds cyber innovation hubs and regional R&D. Enterprises, on the other hand, are investing reactively in EDR, zero trust architectures, and supply chain risk tools. Their spending is often driven by customer compliance demands, cyber insurance eligibility, or breach events. Startups and SMBs gravitate toward cloud-native and open-source platforms, while larger corporations seek out AI-powered security orchestration. This dual-track investment model accelerates overall cyber maturity—but leaves coordination gaps.
-
APAC’s cyber workforce stands out due to its high demand for bilingual skills, regional certification knowledge, and exposure to diverse regulatory environments. Unlike Western markets where frameworks are standardized, APAC professionals must adapt to country-specific privacy laws, from Singapore’s PDPA to India’s DPDP Act. There’s also a stronger emphasis on SOC roles and cloud engineers, as these are the most in-demand positions across India, Singapore, and Australia. Moreover, due to talent shortages in certain areas, many APAC companies hire remotely, increasing the value of professionals trained on localized labs and APAC-specific breach simulations, like those in the ACSMC certification.
-
While global certifications like CISSP and CEH are still respected, region-specific certifications are gaining ground. In 2027–2028, hiring managers across Singapore, India, and Japan are prioritizing programs aligned with local laws and industry norms. For example, CISA-India Special Track addresses compliance with the DPDP Act, while ASEAN-CERT programs offer cross-border threat response training. The Advanced Cybersecurity & Management Certification (ACSMC) by ACSMI is among the few programs built entirely around APAC threat intelligence, multilingual SOC labs, and data governance training tailored to the region. Professionals with both global and regional credentials are the most competitive in today’s hiring pipeline.
-
Breach underreporting in APAC stems from a mix of cultural hesitation, legal ambiguity, and regulatory gaps. In collectivist cultures like Japan and South Korea, public breach disclosure is seen as a reputational failure, often leading companies to contain incidents internally. In countries like Indonesia or Malaysia, lack of enforcement or unclear thresholds result in many breaches going completely unreported. Unlike GDPR in Europe, most APAC jurisdictions lack consistent enforcement timelines or fines, reducing urgency. This leads to incomplete threat sharing, weakens CERT coordination, and prevents other organizations from learning from known attack vectors—a systemic weakness in the region.
-
Local startups in APAC are booming due to underserved mid-market demand, localized compliance needs, and government-backed innovation grants. Countries like Singapore offer cyber R&D incentives, while India’s massive digital footprint creates opportunities for vendors focused on automation and cost-efficiency. These startups often outcompete global firms by offering regionally priced, language-supported, and regulation-aware tools. For example, companies like Horangi and TAC Security are gaining traction in cloud posture and vulnerability management by addressing local threat models, something international players overlook. The rise of APAC-based venture capital in cybersecurity is also helping these vendors scale without leaving the region.
Final Thoughts
Asia-Pacific isn’t just catching up—it’s redefining the global cybersecurity playbook. The region’s complexity is its power: fragmented regulations, aggressive digital expansion, and varied threat surfaces make APAC both a target and a testing ground. From nation-state espionage to mobile-first infrastructure risks, APAC demands strategies that are local in context and global in execution.
Whether you’re a multinational expanding into the region or a local enterprise navigating policy shifts, your success depends on APAC-specific knowledge, talent, and tooling. The old playbook doesn’t work here. You need frameworks that account for language barriers, diverse legal systems, and high-velocity tech adoption.
This is exactly why the Advanced Cybersecurity & Management Certification (ACSMC) by ACSMI exists. It’s not just a course—it’s a strategic accelerator for professionals aiming to lead, build, and secure in Asia-Pacific. The threats are real. But so is your edge—if you know how to use it.
